 Itnetic Technologies
Platform
One edge network. Every layer of defense.
Point your domain at Itnetic and every request flows through a single edge pipeline — challenge gate, behavioral signatures, WAF, rate limits and cache — before it ever reaches your origin.
The edge pipeline
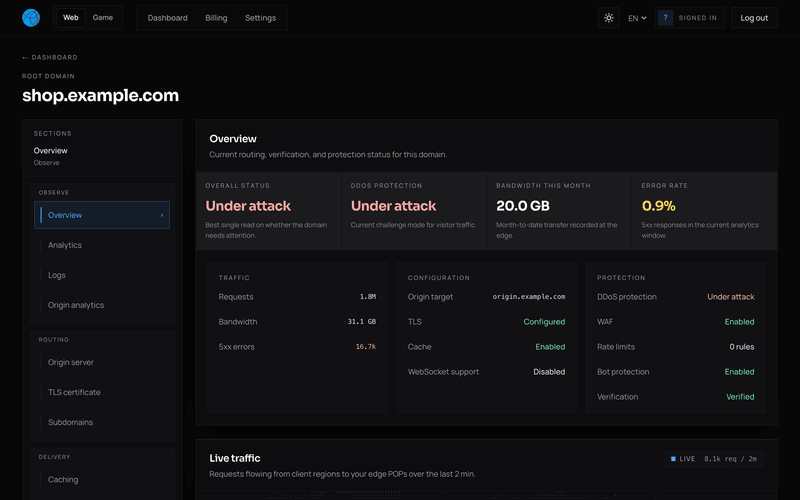
Protection runs before your origin does
Every request passes the full pipeline — challenge gate, behavioral signature, route match, rate limit, cache — and reaches your origin only if it earns it.
- Points of presence across Europe, North America and Asia Pacific.
- Volumetric floods absorbed by the upstream backbone before they reach the app layer.
- Repeat offenders dropped at the kernel with nftables — no per-request cost.
Behavioral detection
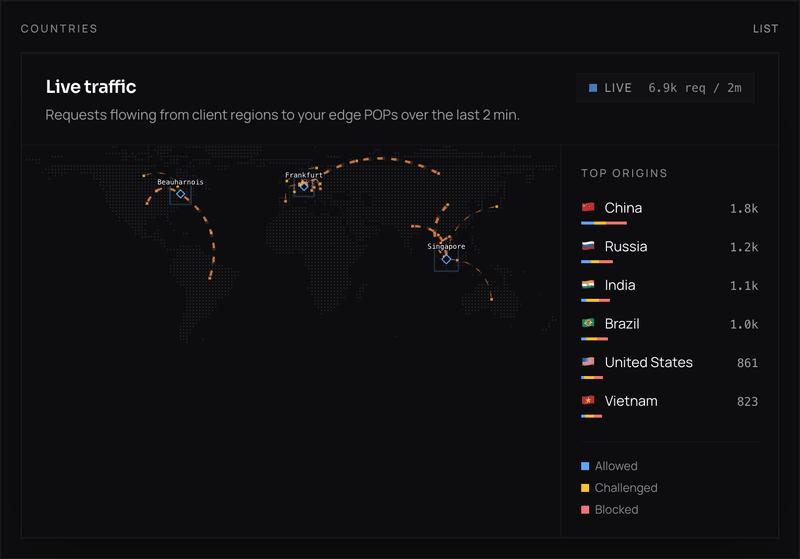
Catches attacks that look human
Each request is profiled by path, header and TLS fingerprint, and spikes trip protection at the edge in seconds — no round-trip to a control plane.
- Behavioral signatures match the shape of an attack, not just its volume.
- Adaptive local detection flips to challenge mode within a second of a spike.
- A lightweight cryptographic challenge replaces CAPTCHAs — real visitors never see it.
Web Application Firewall
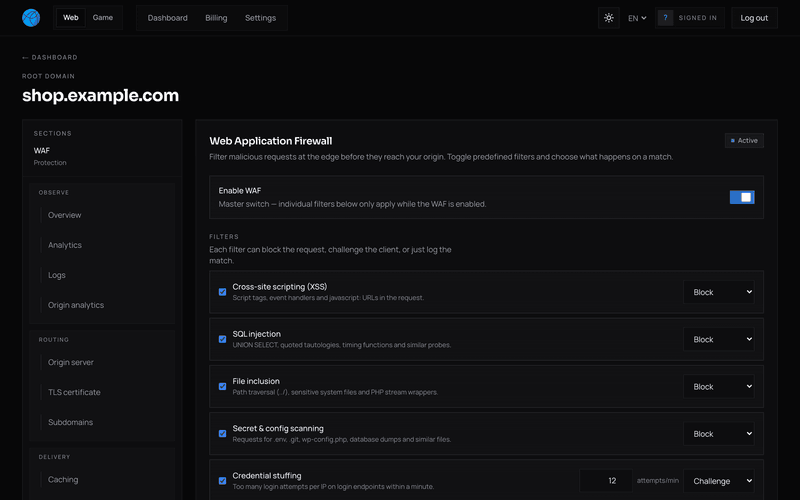
A firewall you actually control
Managed filters cover the OWASP classics out of the box; your own rules layer on top, matching path, header, method, country or fingerprint.
- Managed OWASP filters, each set to block, challenge or log.
- Custom rules with typed fields — no fragile freeform syntax.
- IP reputation and verified-bot allowlist enforced ahead of your rules.
TLS & certificates
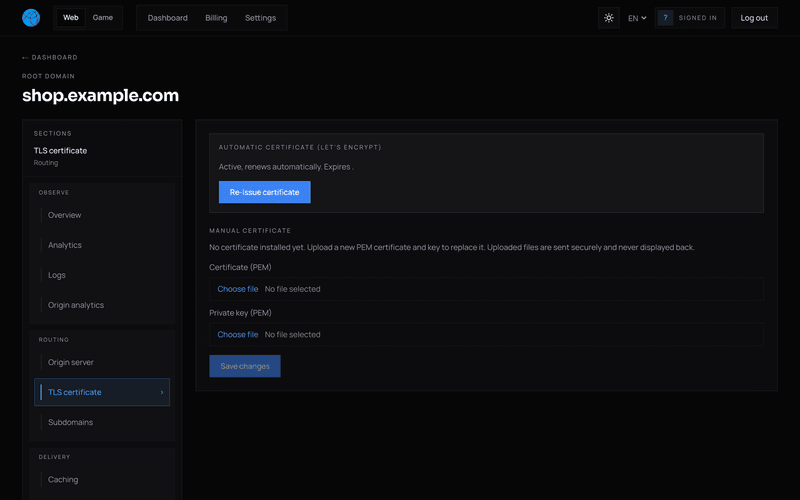
HTTPS handled for you
Every domain gets a Let’s Encrypt certificate that issues and renews itself — or upload your own PEM and we serve it at the edge.
- Automatic issuance and renewal, no cron jobs.
- Bring-your-own PEM certificates when you need them.
- Modern TLS terminated at every point of presence.
FAQ
Questions?
How long does setup take?
Two DNS record changes. Most customers are fully protected within five minutes — no hardware, no agents.
Do I have to write rules to be protected?
No. Behavioral detection and managed WAF filters work out of the box. Custom rules are there when you want precise, application-specific control.
Is attack traffic billed against my quota?
No. Attack traffic is scrubbed at no cost to your bandwidth quota — only legitimate, delivered traffic counts.